Secrets Management Best Practices for Production: Storage, Rotation, and Short-Lived Credentials
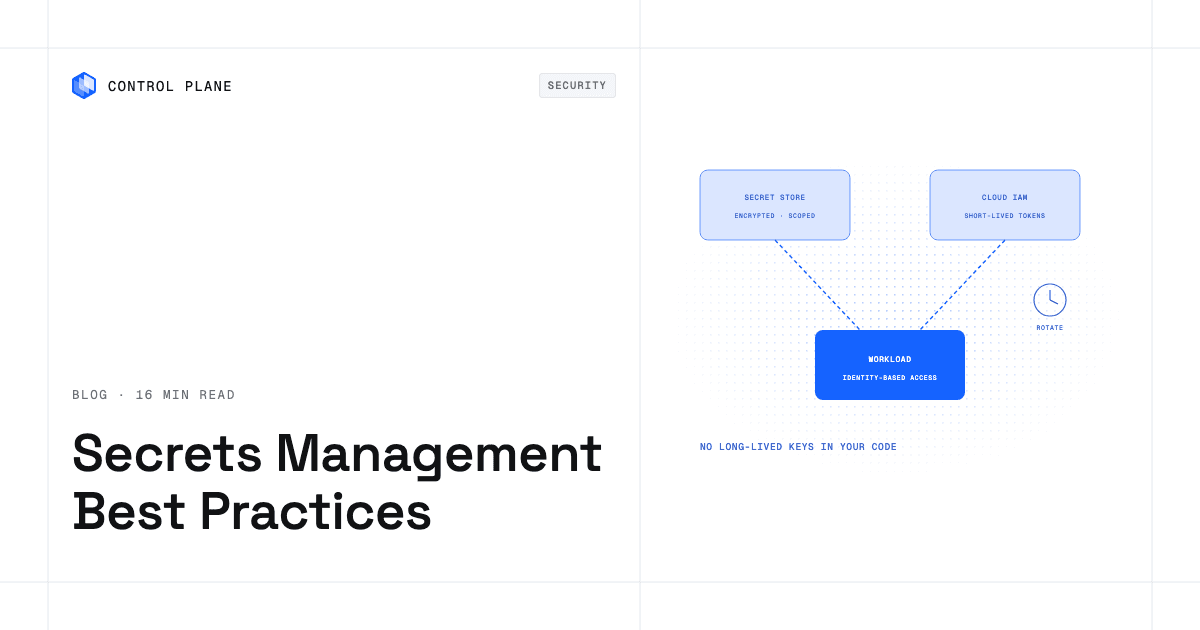
How to store, inject, scope, rotate, and audit secrets in production, and replace long-lived cloud keys with short-lived, identity-based credentials.
How to store, inject, scope, rotate, and audit secrets in production, and replace long-lived cloud keys with short-lived, identity-based credentials.
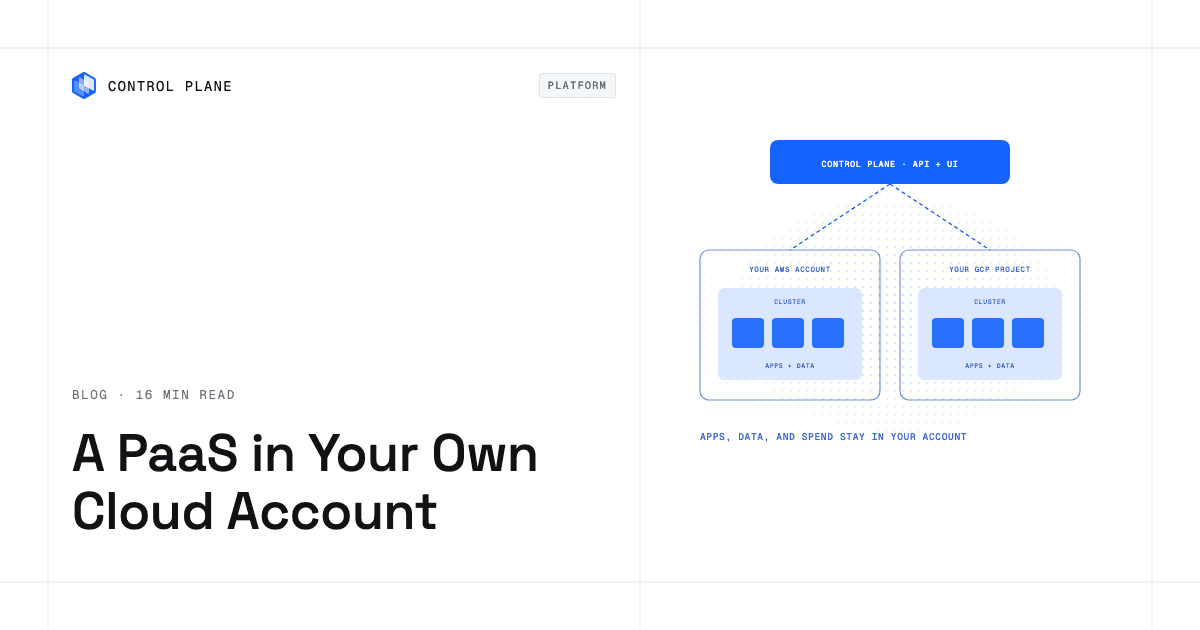
Run a PaaS in your own AWS or GCP account: how BYOC works, four deployment models compared, when BYOC is worth it, and a vendor due-diligence checklist.
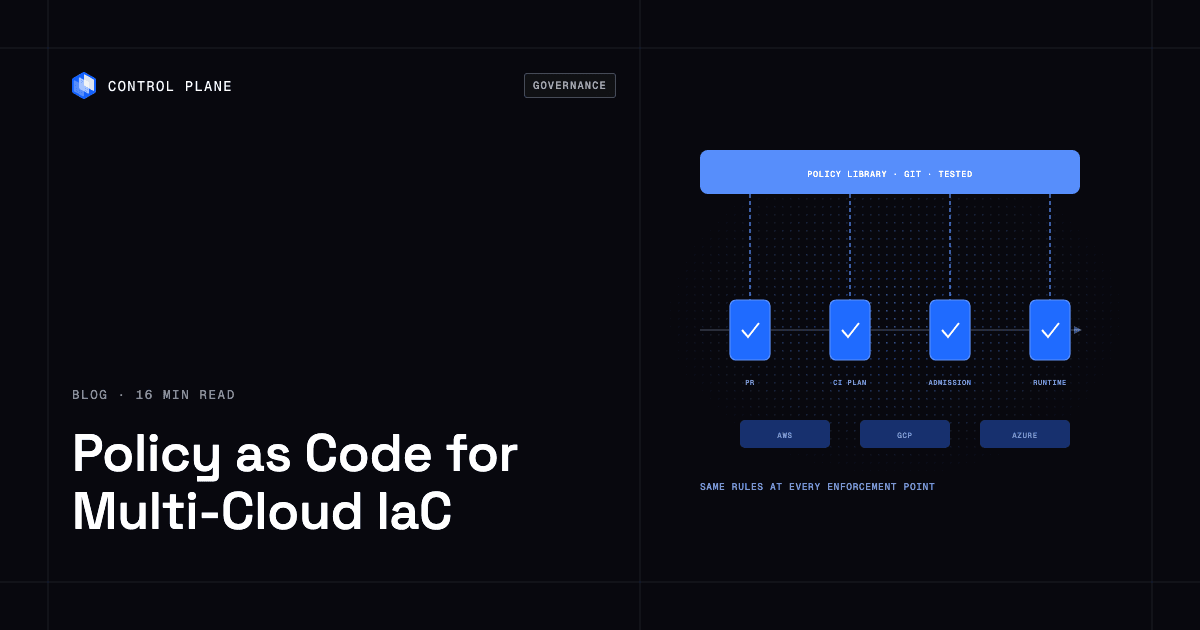
Structure multi-cloud IaC governance with policy as code: four enforcement points, repo layout, IaC and policy tools compared, and a starter policy set.
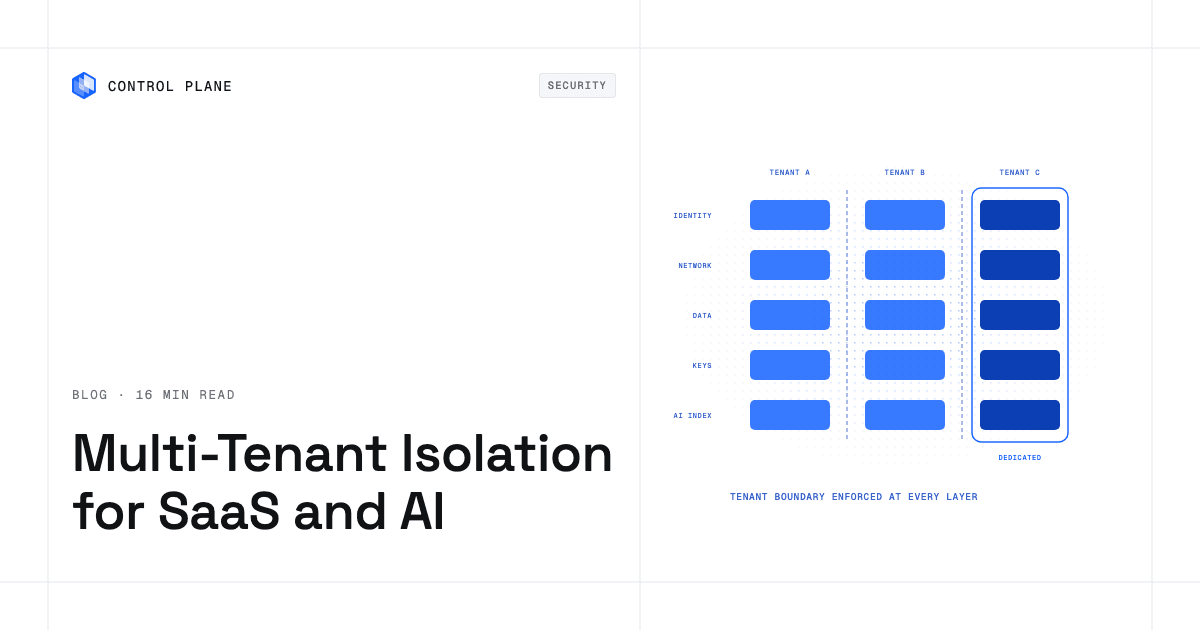
Prevent cross-tenant data breaches in SaaS and AI: silo, pool, and bridge models, BYOK and per-tenant keys, AI data segregation, and a layer checklist.
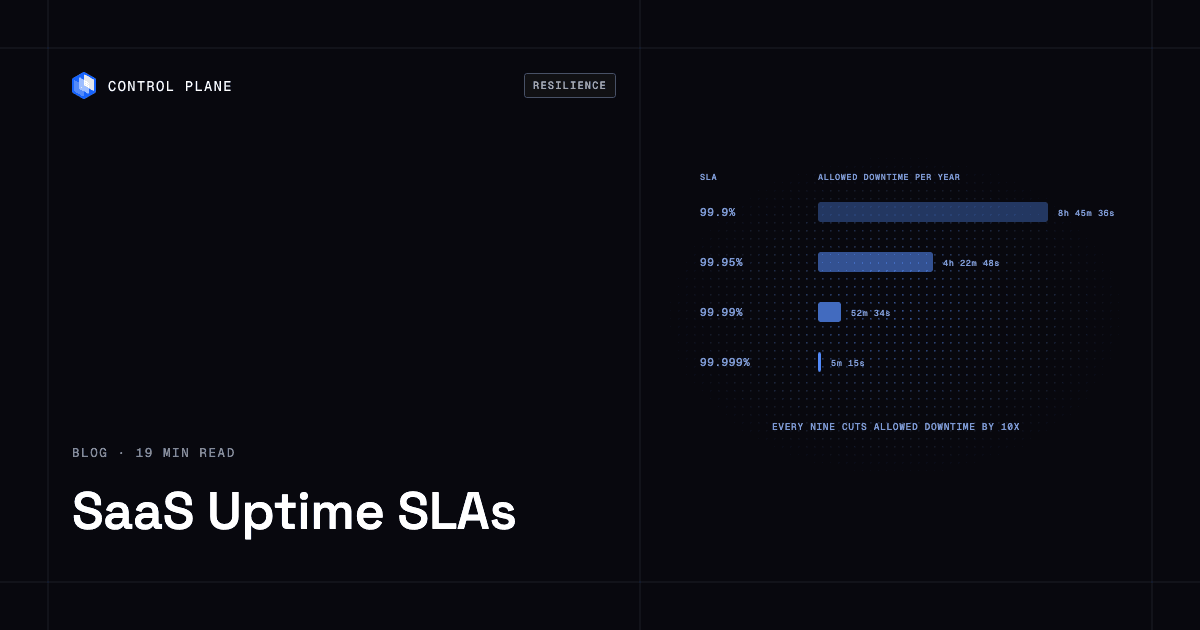
What uptime SLA to offer enterprise customers, exact downtime per nine, how to engineer 99.99%, database failover, failover testing, and vendor questions.
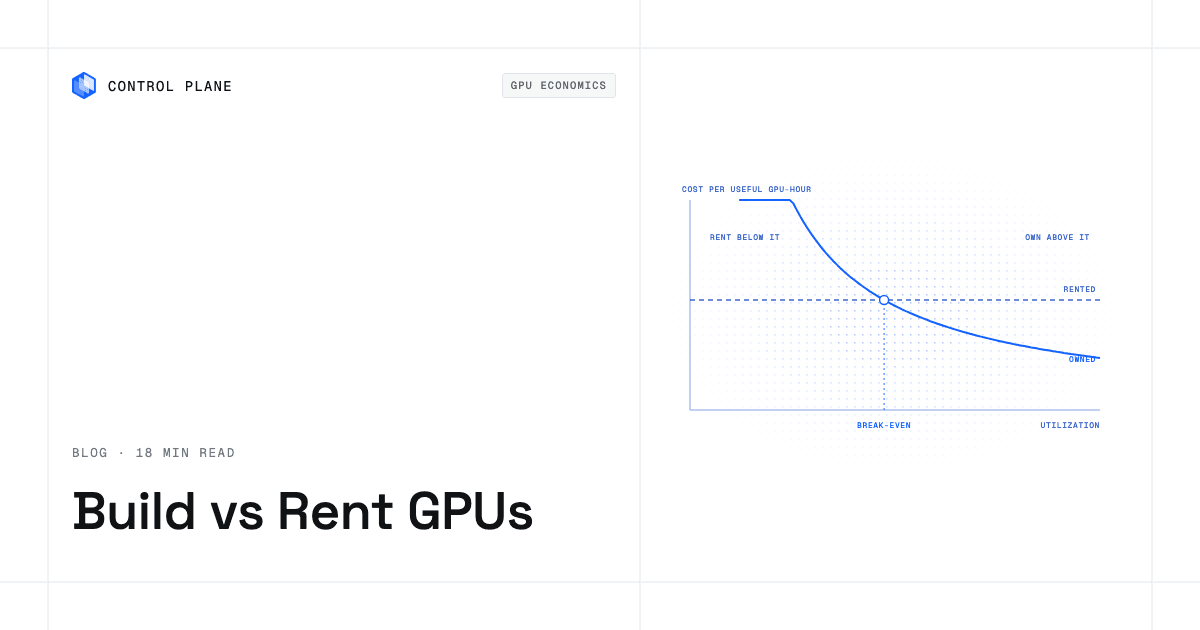
Build vs rent GPUs: a break-even utilization model, a full TCO checklist, neocloud vs AWS costs, procurement and compliance factors, and a hybrid plan.
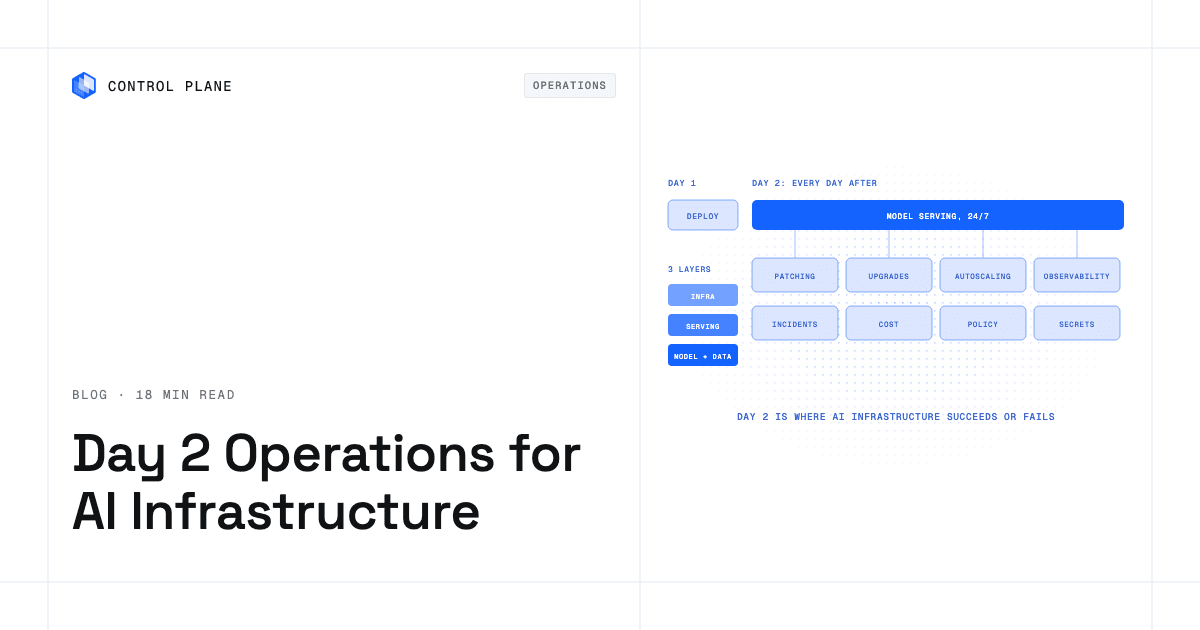
Day 2 operations for AI infrastructure: automate patching and upgrades, add three layers of observability, run incident response, and keep serving up 24/7.
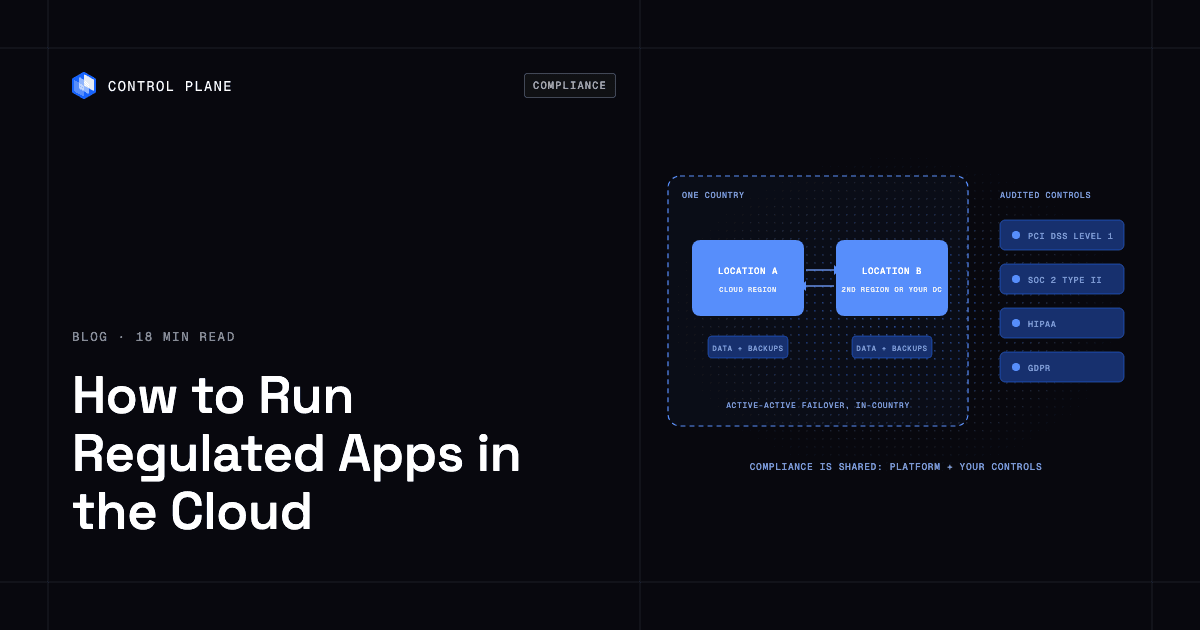
Run regulated apps in the cloud: verify SOC 2, HIPAA, and PCI DSS platforms, keep data in one country with failover, and use a compliance checklist.
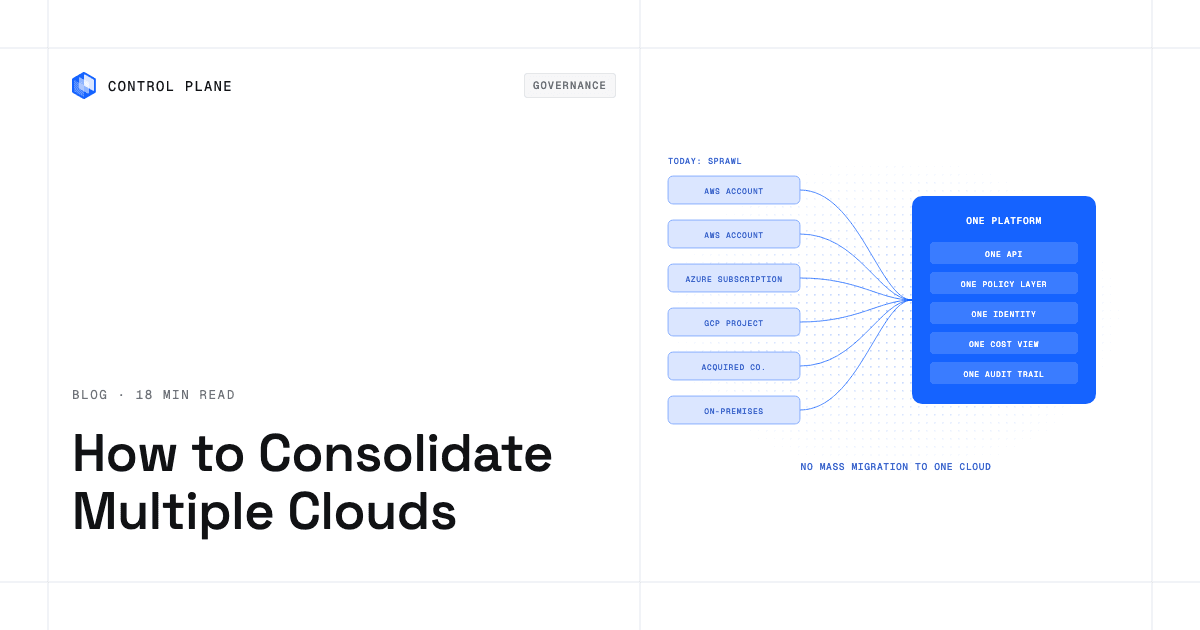
How to consolidate multiple cloud providers and accounts into one governed platform: a step-by-step program, ROI model, merger playbook, and checklist.
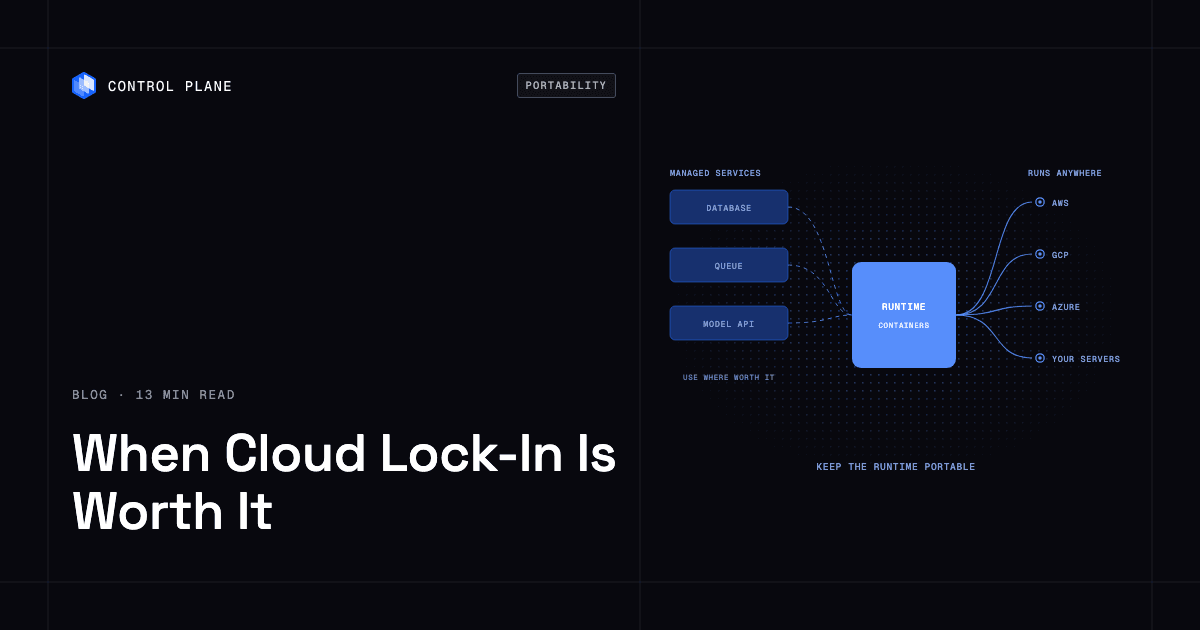
When is cloud lock-in worth it? A decision framework for managed services vs portability, open-source alternatives, exit clauses, and an exit plan.
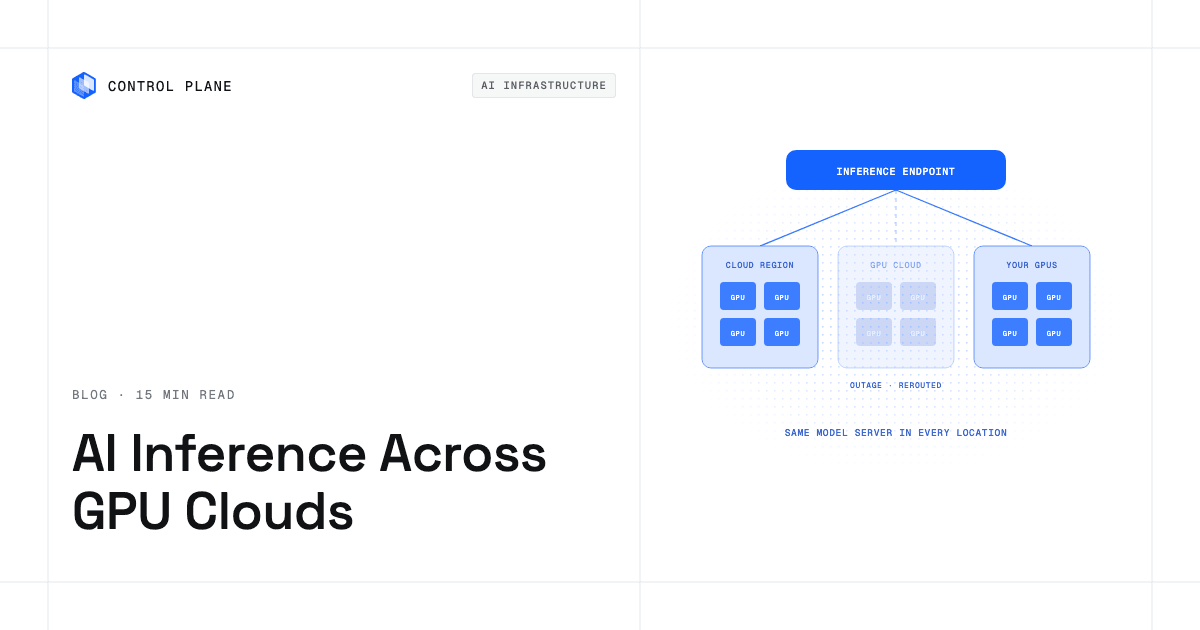
How to run AI inference across multiple GPU clouds in 2026: fail over between GPU providers, burst from your own GPUs, and move as prices change.